Detection of pre-installed malware on low-cost phones in more than 150 countries


(Dan Tri) - Security experts discovered that thousands of cheap Android phones were pre-installed with malicious code before reaching users. This campaign was recorded in more than 150 countries in about 2 years.
Bitdefender has just warned about a malware campaign called Midnight Mimosa on a number of low-cost, multi-brand Android phones using the MediaTek platform. Notably, the malicious code was built into the device's system software before being sold to the market.
According to experts, some affected devices use model names imitating high-end phones, such as S24 Ultra, S25 Ultra, S26 Ultra or i17 Pro Max.
It should be noted that these are device names recorded during the analysis process, which does not mean that all products with similar names contain malicious code.
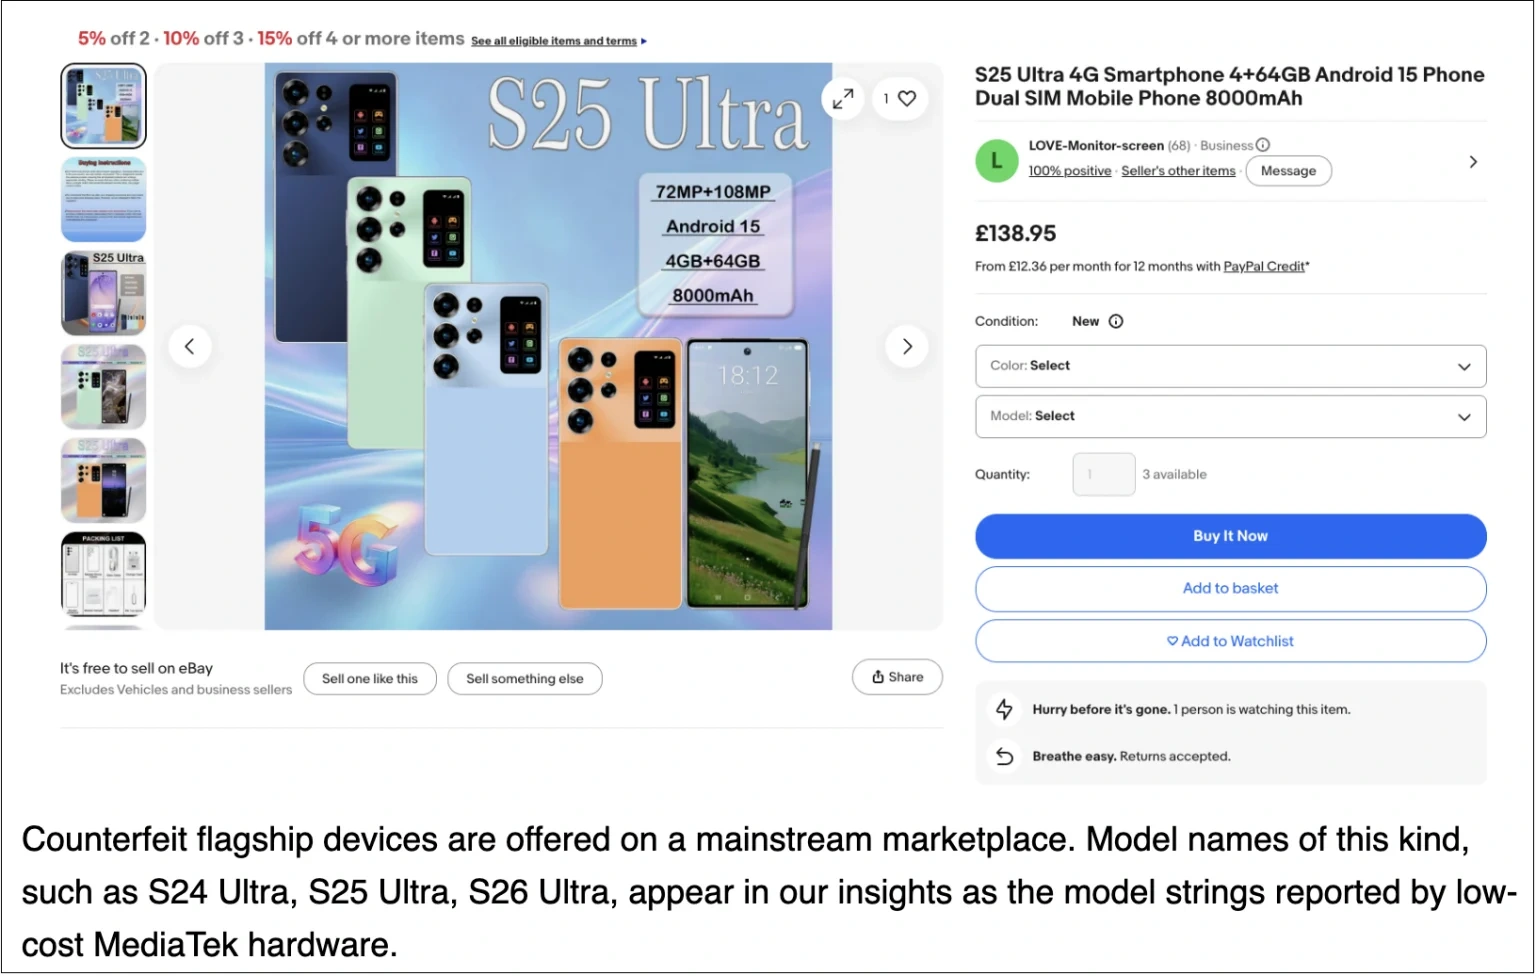
A low-cost phone model using a fake name of the Galaxy S25 series (Photo: Bitdefender).
Bitdefender said it has recorded thousands of affected devices in more than 150 countries over about 2 years. Mexico, France, Italy, the US and Germany are the countries with the highest number of recorded cases.
During analysis, experts discovered a system component with the package name "com.android.system.lite". This component disguises itself as an Android system application, is built into the firmware and has system-level operating rights, so users cannot remove it in the usual way.
According to Bitdefender, Midnight Mimosa malware can silently install and remove applications, grant permissions to other applications and download code remotely. Thereby, the person behind it can deploy ad fraud activities, create fake clicks or turn the device into a network traffic relay node in botnet networks.
These behaviors can cause the device to consume resources for background activities, while also creating risks to users' privacy and information security.
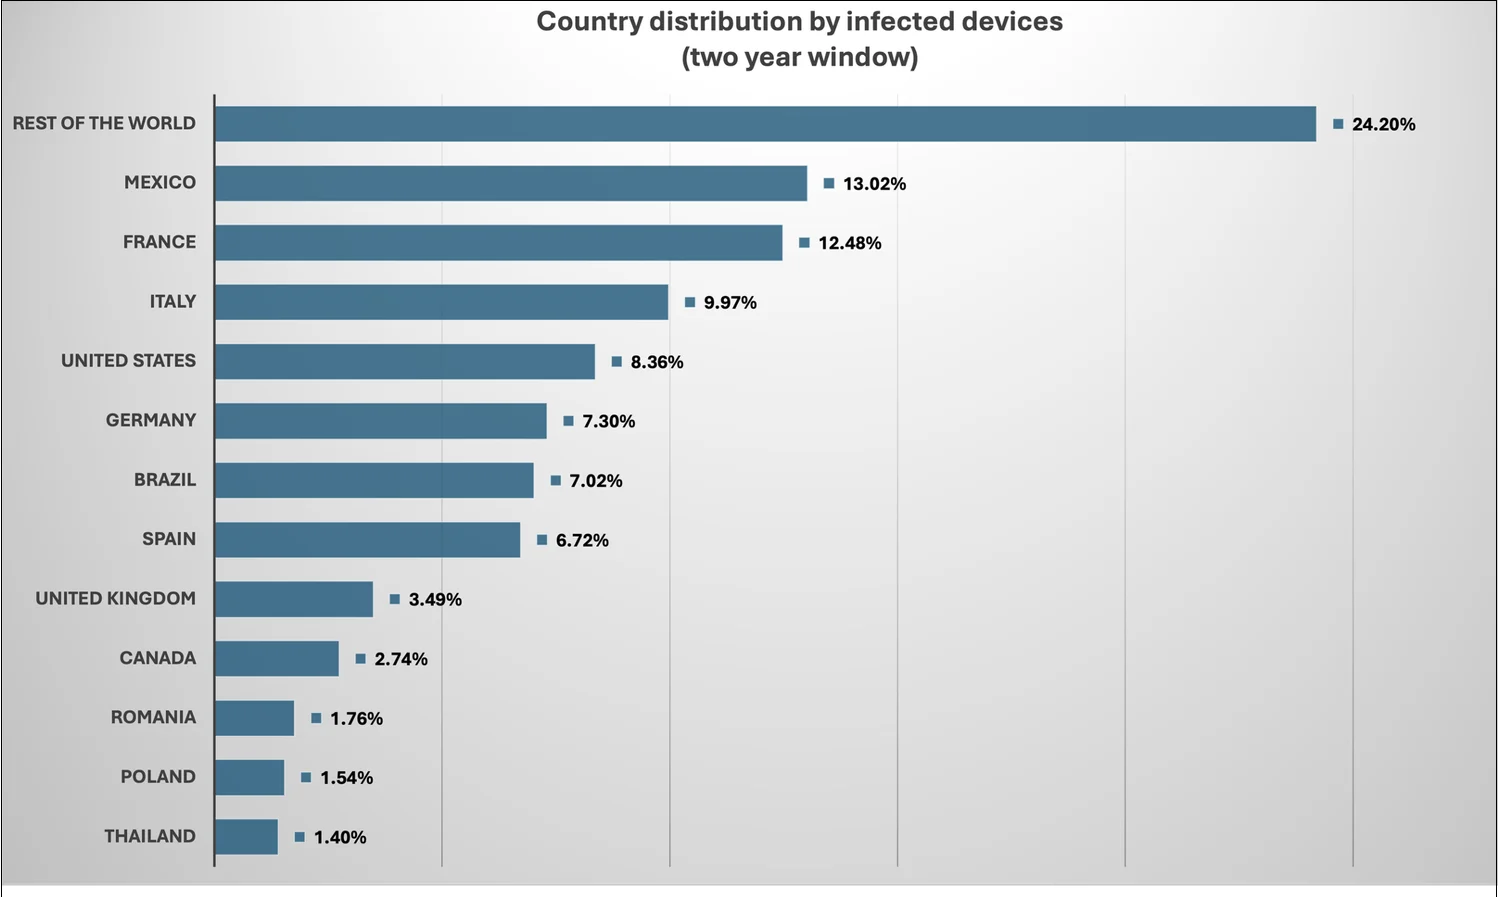
Percentage of countries affected by low-cost phone models with pre-installed malware (Photo: Bitdefender).
Bitdefender also discovered firmware on some devices signed with a certificate bearing the name Shenzhen Zediel. However, experts have not yet determined which party put the malicious code into the firmware, nor do they have enough evidence to conclude that the certificate owner is involved or knows about this.
According to Bitdefender, malicious code can be introduced into the device at some stage in the supply chain, such as when integrating firmware or completing the product. Determining the exact responsible entity requires additional information beyond the scope of existing technical analysis.
For people using the affected device, removing the malicious code is not simple because this component is located in the firmware or system partition. It is difficult for users to handle it by uninstalling the application or restoring normal factory settings. Fixing may require clean firmware from the vendor or the assistance of a qualified technician.
This is not the first time malicious code has been discovered pre-installed on technology devices before reaching users. Previously, many reports also recorded cases of mobile devices and computers being integrated with malware during the production or distribution process.